

Before you start
- Ask Lobyco for the authentication configuration of the environment. Lobyco creates a multi-tenant app on its side and sends you three values:
lobyco_app_id, the application id of the Lobyco multi-tenant app.lobyco_app_name, its display name.lobyco_app_uri, its application id URI, which becomes the token scope.
- You must be a Global Administrator, an Application Administrator or a Cloud Application Administrator in your tenant, because application permissions take admin consent.
The procedure
1
Import the Lobyco app into your directory
Create a service principal in your tenant that represents the Lobyco multi-tenant app. Until it exists, the Lobyco app and its roles are not visible in your tenant. Run this in PowerShell:lobyco_app_name.2
Register the client app
Register the single-tenant app that represents your service. Go to App registrations in the Azure portal and choose New registration.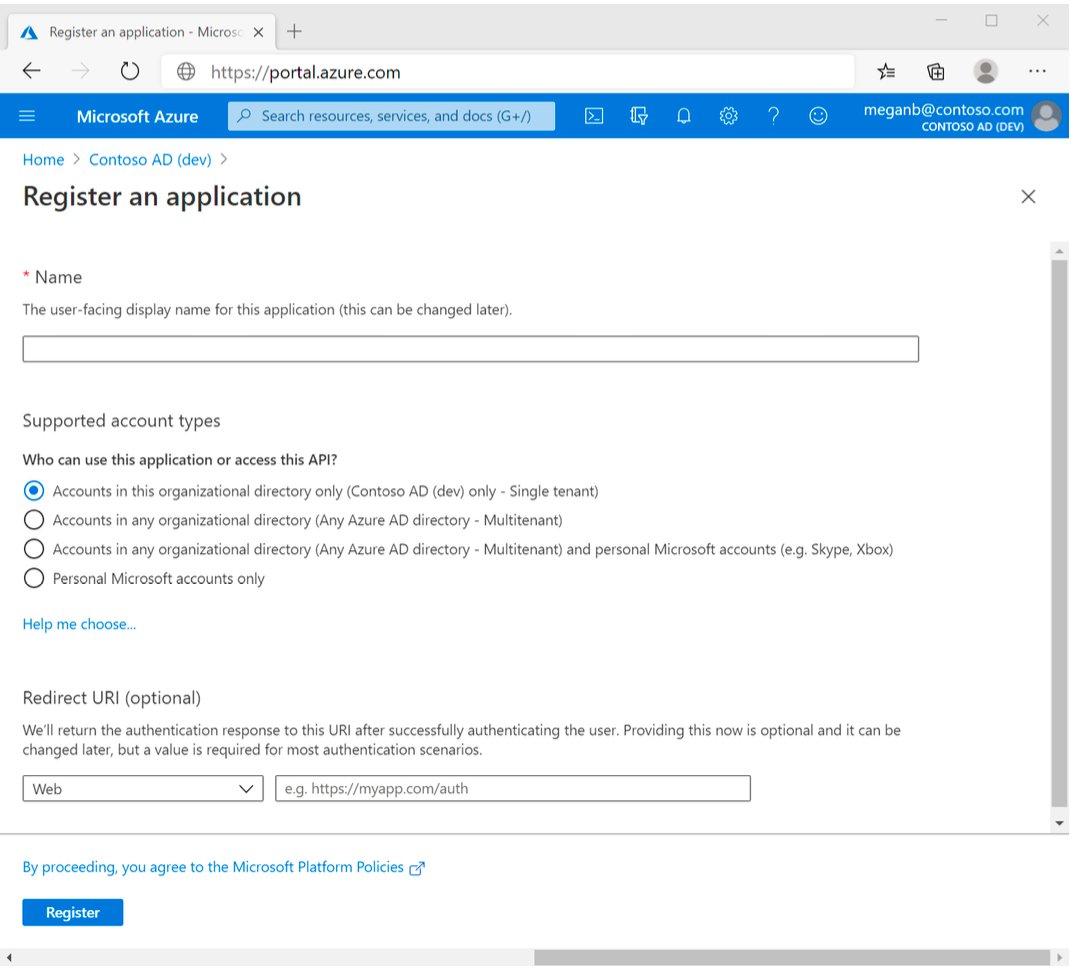
- Name: a name that says what it is and which environment it serves, such as
lobyco-api-client-appfollowed by the environment name. - Supported account types: Accounts in this organizational directory only.
- Redirect URI: leave it empty. The client credentials flow does not use one.
client_app_id. The token request uses it.3
Add a secret or a certificate
A confidential client authenticates as itself, without a user, so it carries a credential of its own. Under Certificates & secrets, add a client secret or upload a certificate.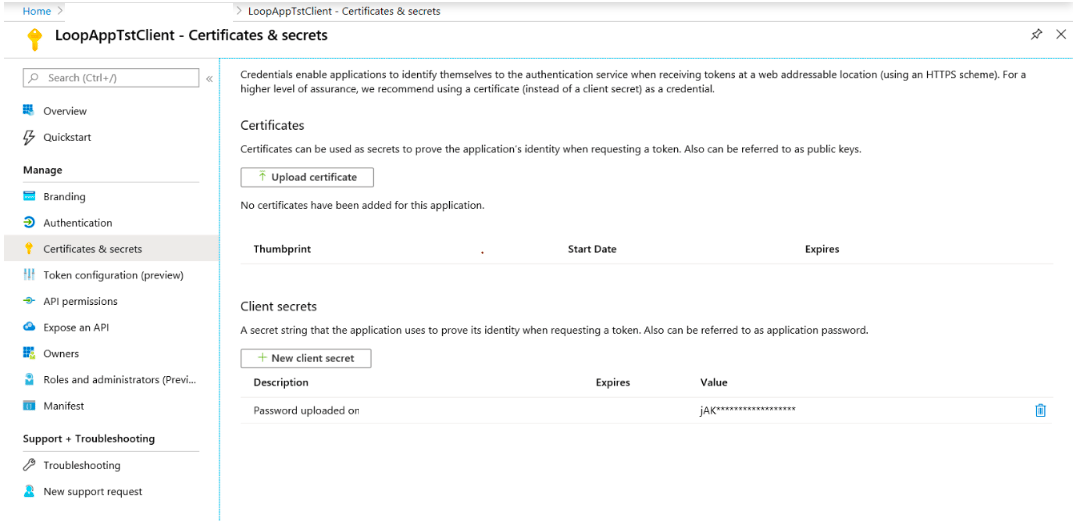
client_app_secret. The portal shows it only once.4
Grant the application permissions
Under API permissions, choose Add a permission and open the APIs my organization uses tab. Search for the Lobyco app bylobyco_app_name or lobyco_app_id.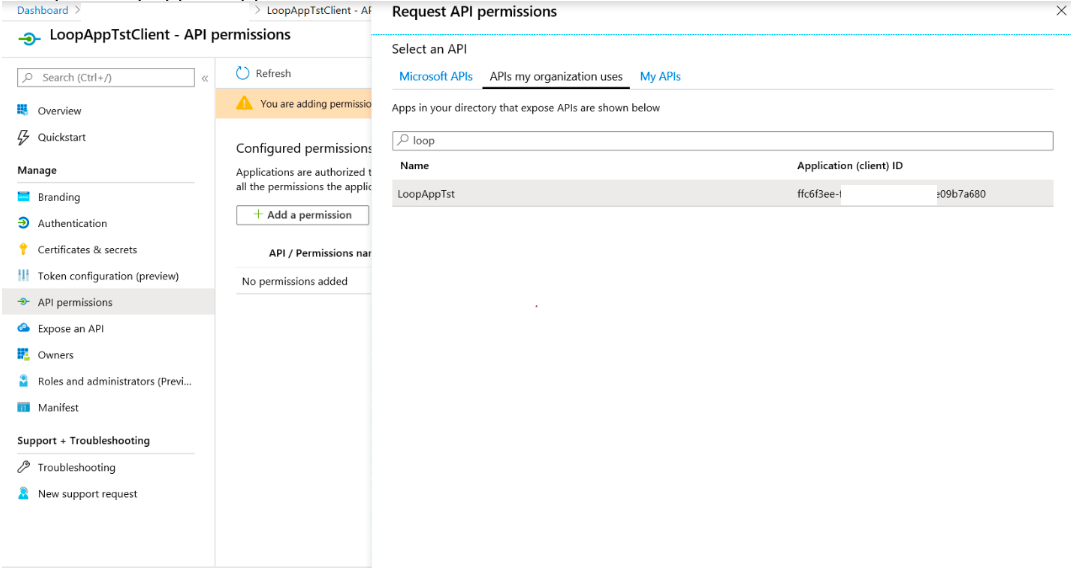
Games.MobileAPI.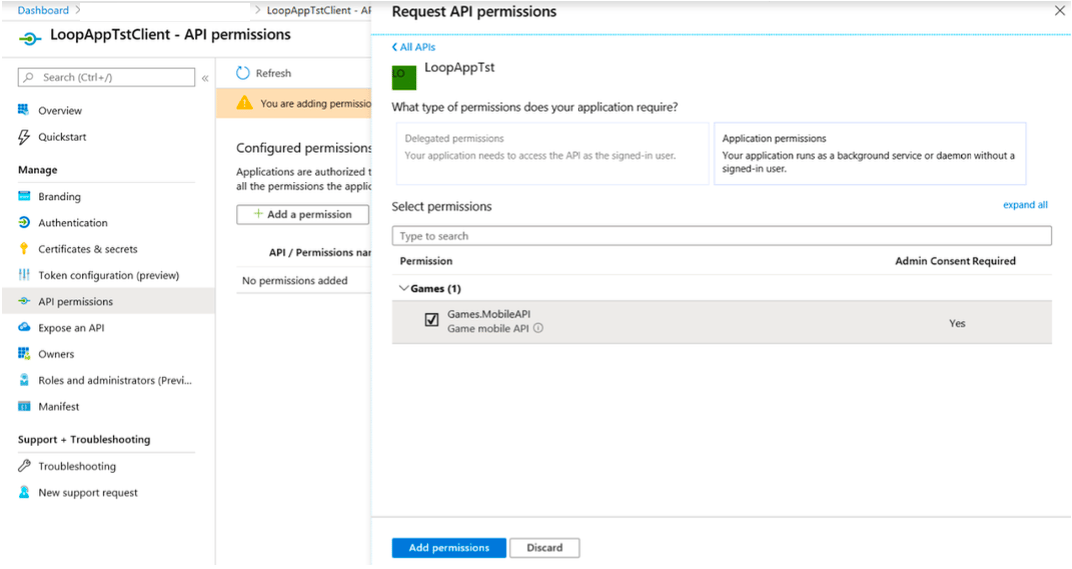
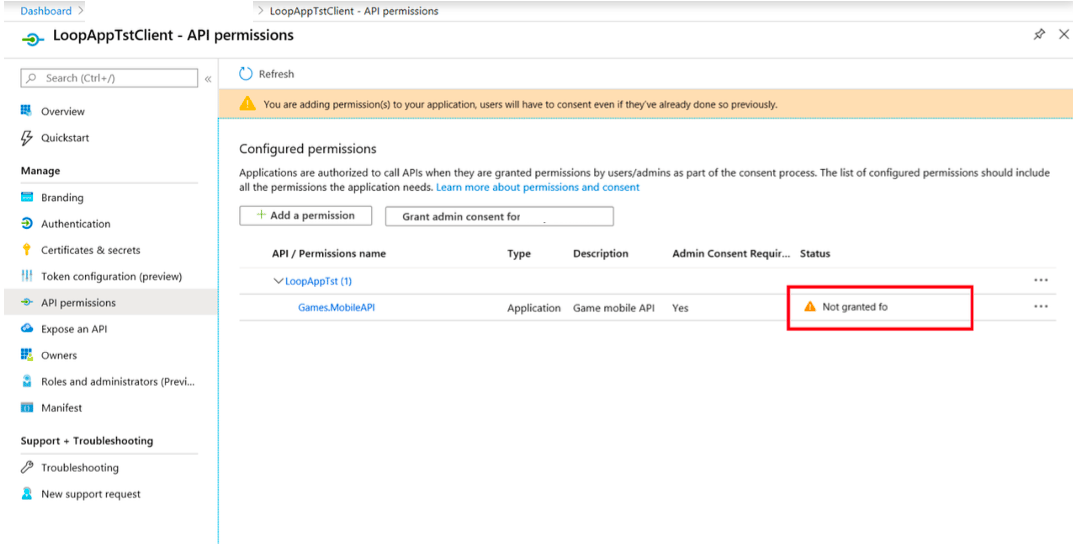
5
Set the token version in the manifest
Open Manifest, setaccessTokenAcceptedVersion to 2, and save.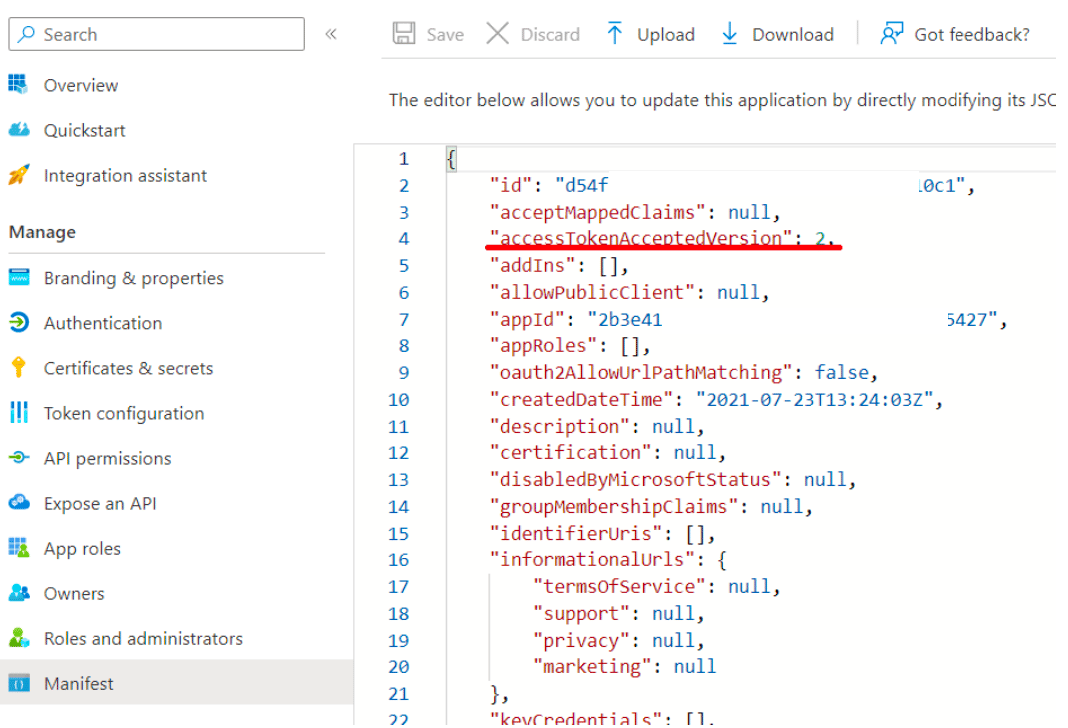
6
Request a token and check its roles
Request the token as described on Lobyco tenant authentication using client credentials flow. The request is the same; use your own tenant id asclient_tenant_id, and the client_app_id and client_app_secret you recorded.Decode the token at jwt.ms and check that the roles claim lists every application permission you granted. A token from this setup looks like this:aud is the Lobyco app, iss is your tenant, and roles carries the permissions. With this token, the first call to a Lobyco API returns the normal response, not 401 Unauthorized.Failure and edge cases
A refused token request, an expired token or a401 Unauthorized are the token request’s own failures, covered on Lobyco tenant authentication using client credentials flow. Two cases are specific to this setup.
Which scope do I request?
Which scope do I request?
Always
{lobyco_app_uri}.default, whatever permissions you selected. The roles come from the consent, not from the scope string. A scope that names a permission instead is refused.Why is a role missing from the token?
Why is a role missing from the token?
Admin consent was not granted for it, or the token was issued before consent. Grant consent and request a new token.
Related
- Lobyco tenant authentication using client credentials flow — the token request and the
Authorizationheader, shared by both setups. - API authentication — the two schemes, and when to choose this setup.
- Access to Lobyco Admin Portal — the other Azure AD setup, for admin users rather than services.